Maintenance Window policies are coming to Intune

“We got Intune maintenance window policies before we got GTA 6”. Well, not quite, it’s in development.

But Marcus, we already have that in Intune with Active Hours? Again, not quite. Active Hours define when Windows should avoid disrupting the user, think restarts. Whereas Maintenance Windows define when Intune should perform scheduled update activity.
Anyone who works in retail, manufacturing or has critical near 24/7 devices such as control stations and kiosks will have had the discussion “How can I guarantee no update activity will occur outside of a maintenance window?”.

And had the Service Desk ticket logged “I had to restart my device and updates are installing so now I can’t perform this critical function for the business!”.

Microsoft says:

“Microsoft Intune will introduce maintenance windows to help you schedule firmware, driver, and operating system updates on Windows devices. You’ll be able to choose supported update operations and configure a start date, start time, duration, and repeat schedule.

You’ll create a maintenance windows profile in the Microsoft Intune admin center to define when update activity should take place. Scheduling options will include daily, weekly, and monthly recurrence, so you can align update activity with your organization’s planned maintenance periods. This initial release will focus on updates; it won’t include maintenance windows for application installations.”

That last bit is interesting. A clear intent to make this available for that other potentially user impacting workload in Intune, app deployments. Those of us long enough in the tooth will see this not as a new feature, but rebirthing one that has been in the Microsoft Endpoint Management ecosystem for nearly 20 years via ConfigMgr.

While most organisations have become accustomed to the ‘let Windows opportunistically carry out update activity’ mantra, I believe that choice is key. Let each organisation decide for each device what the update strategy is, and give them the tools to do it.
Microsoft Foundry model router now has 35 models

Microsoft Foundry model router picked up another eight models this month, taking its routing pool to 35 models.

The new additions include gpt-6-astra, three Claude 5 models, Grok 4.6 and three Fireworks models.

Microsoft Foundry model router automatically chooses an appropriate model for each request from a pool of supported models. The cost benefit is that you do not have to send every prompt to the largest or most expensive model. Simpler requests can be handled by cheaper models, while more capable models can be selected when the task needs them. That can reduce overall model spend without you having to build and maintain the routing logic yourself.

Purview DLP is rolling out to Microsoft Cowork

“How do I protect sensitive information when using Microsoft Cowork?”

Just when organisations were getting used to Microsoft Copilot, Cowork comes along and resets the enablement clock. Or does it?

The good news is that you don’t necessarily need to start again with a completely new set of data protection controls.

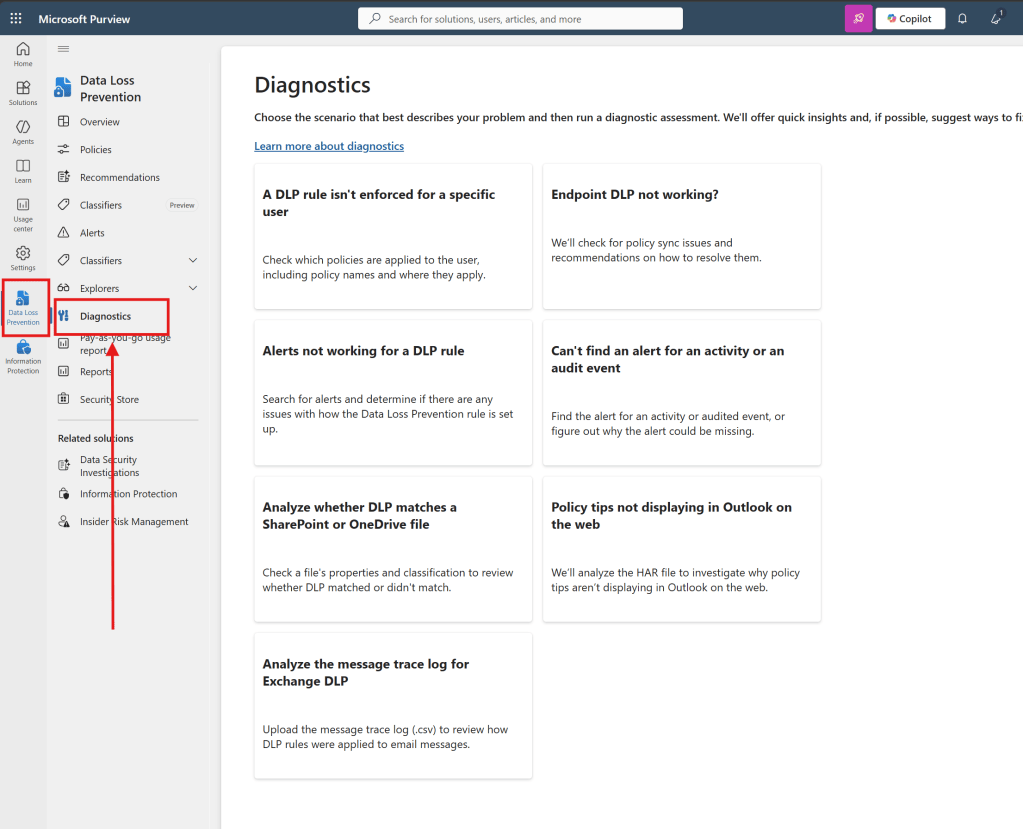
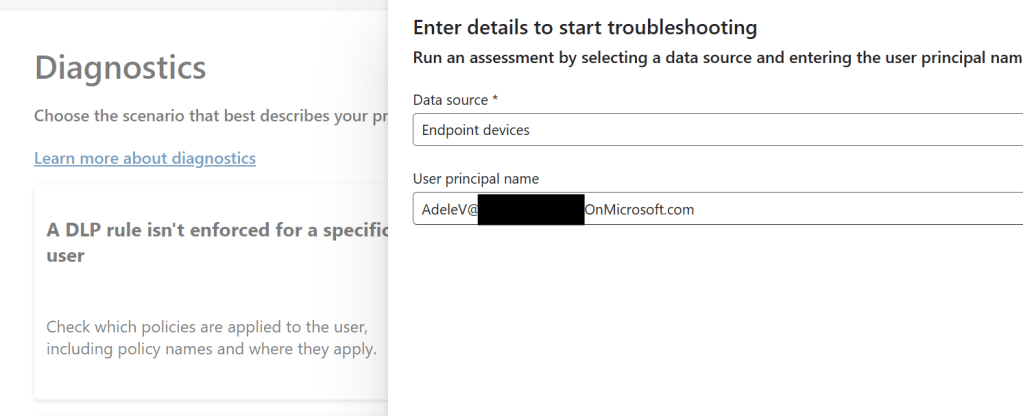
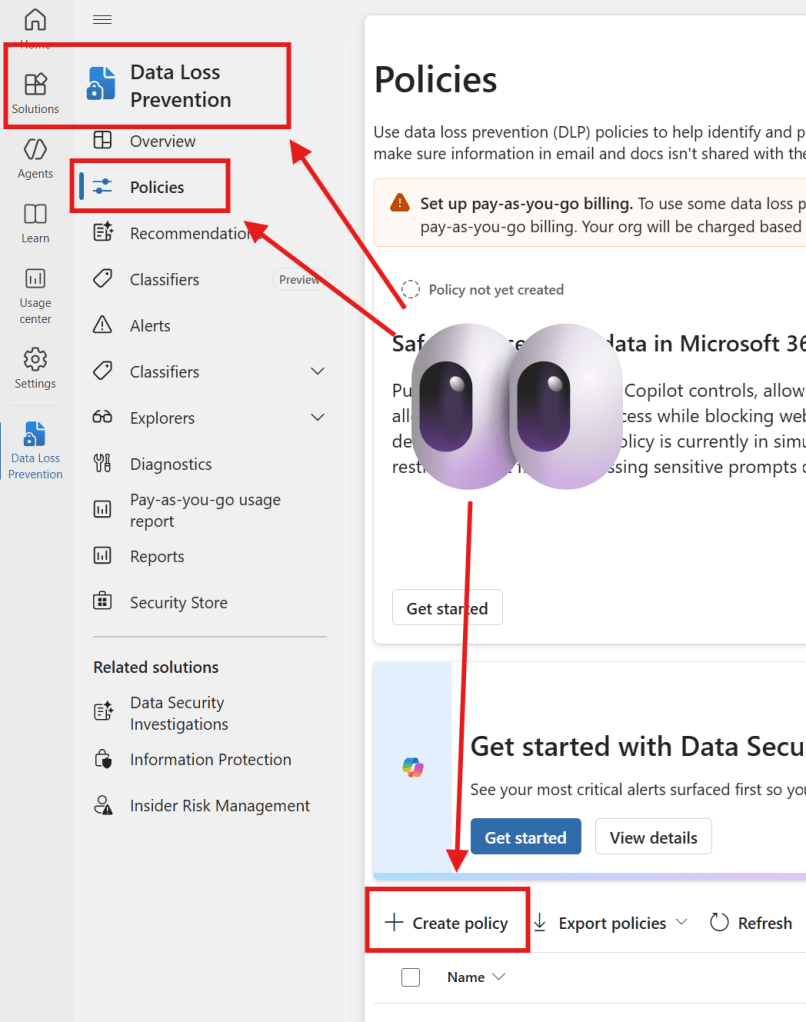
Microsoft Purview DLP is expanding to Microsoft Cowork. This is currently in rollout.

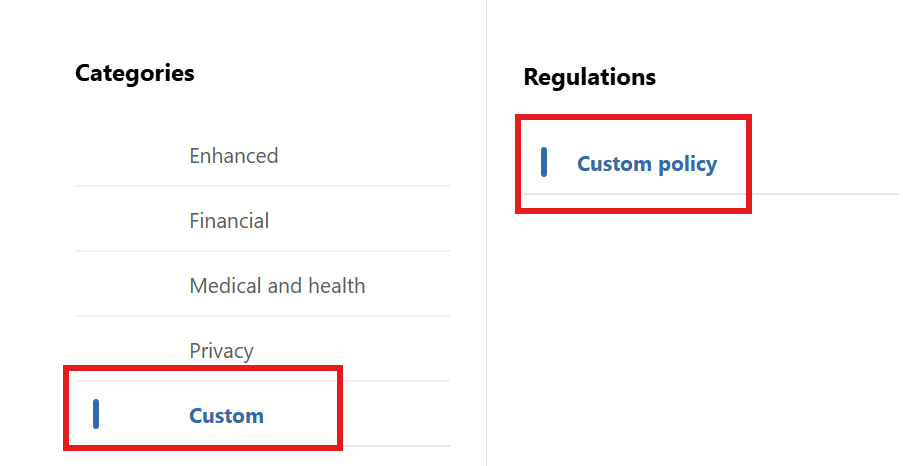
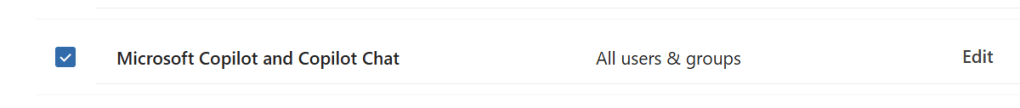
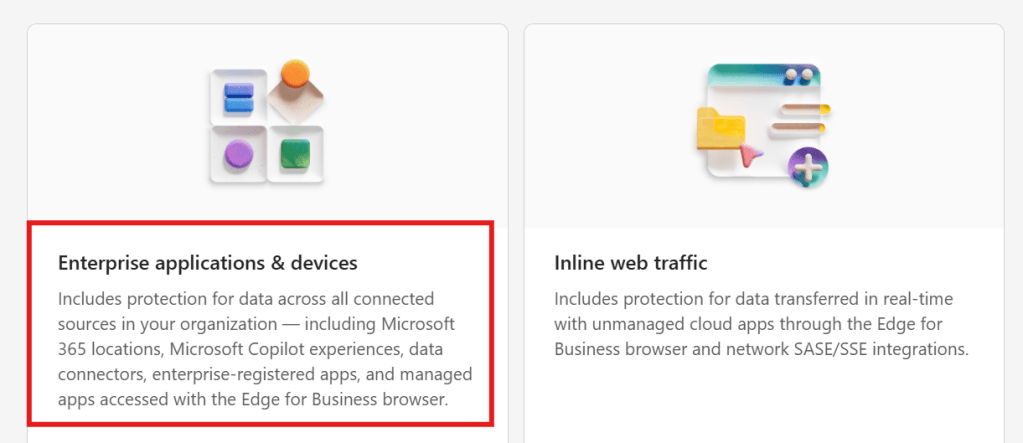
This means organisations can use the same DLP policies across Copilot and Cowork to help control how sensitive information is used. And this one Microsoft made simple, we use the same DLP location “Microsoft Copilot and Copilot Chat” as we use for Copilot DLP policies.

That includes:

🔐 Controlling whether content with specific sensitivity labels can be used as a knowledge source

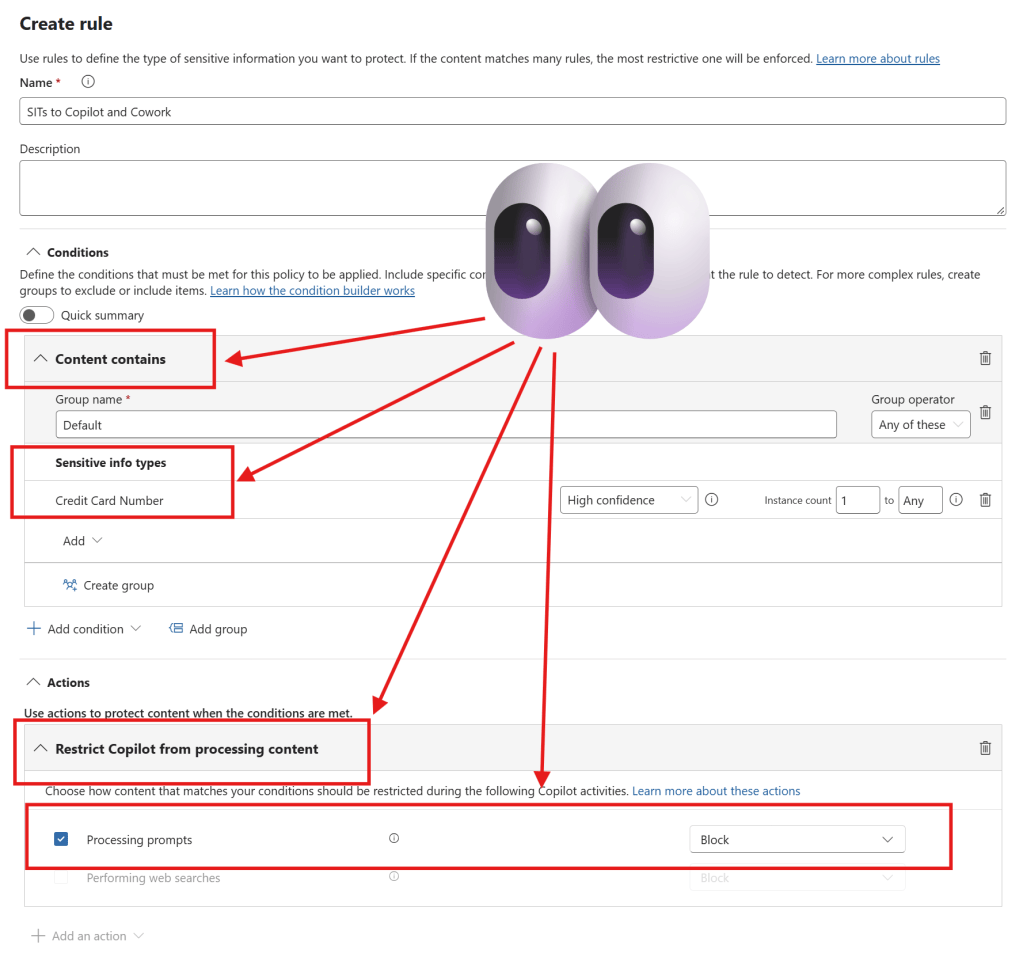
🔐 Detecting sensitive information types within prompts

🔐 Preventing sensitive prompts from being sent to Bing web search

Sensitivity labels, data classification and DLP are not things you bolt onto AI afterwards. They are part of the foundation for using it securely.

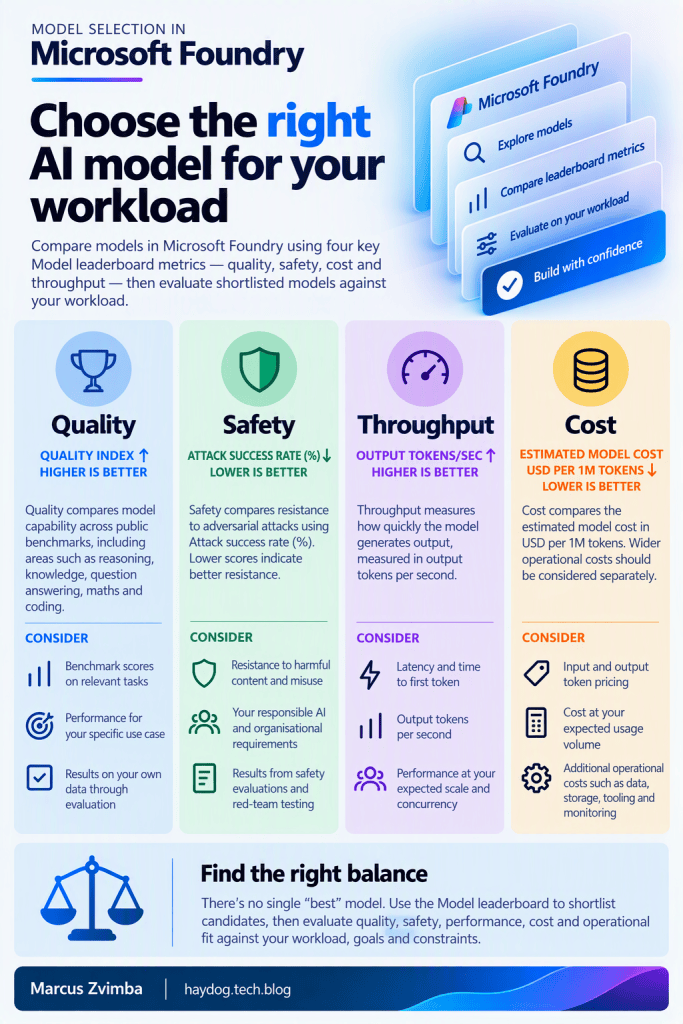
Microsoft Foundry Model Comparison

Quick, Sausage, Tomato, Cucumber – High, Low, High, Low | This is how I remember the four key metrics of Foundry model comparison:

✅ Quality – Quality index: higher is better

✅ Safety – Attack success rate (%): lower is better

✅ Throughput – Output tokens/sec: higher is better

✅ Cost – Estimated USD per 1M tokens: lower is better

Using Microsoft Foundry’s built-in model browser on the Discover > Models tab, you can compare these metrics. This is just the start of the process. Model evaluation is critical, testing the models performance doing the actual task.

Purview Deployment Video Series Part 3 released – SENSITIVITY LABELS

In this video, we build on the data classification work completed in Part 2 and start applying Microsoft Purview Sensitivity Labels to protect organisational data.

We’ll begin by configuring the prerequisites for Sensitivity Labels, including support for PDFs, video files, OneNote, and SharePoint/Teams integration. From there, we’ll explore how labels work, how to design an effective label taxonomy, and how to configure both manual and automatic labelling policies.

In this episode you’ll learn how to:

✅ Enable co-authoring for labelled documents
✅ Enable Sensitivity Labels for PDF files
✅ Enable Sensitivity Labels for video files (MP4)
✅ Enable Sensitivity Labels for OneNote
✅ Validate SharePoint and Teams label support
✅ Understand Sensitivity Label prerequisites
✅ Design an effective label taxonomy
✅ Deploy Microsoft’s default sensitivity labels
✅ Review label groups and label hierarchy
✅ Configure encryption and access controls
✅ Configure content markings and dynamic watermarking
✅ Create custom sensitivity labels
✅ Configure client-side auto-labelling
✅ Configure service-side auto-labelling policies
✅ Publish labels to users
✅ Configure default labels for documents, email and meetings
✅ Require business justification for label downgrades
✅ Understand label inheritance from attachments and meeting content
✅ See the end-user labelling experience in Microsoft Word

You’ll also gain an understanding of the difference between classification and protection, how label groups affect the user experience, and how Sensitivity Labels work alongside trainable classifiers and auto-labelling to build a scalable information protection strategy.

This video is part of a larger series covering:

🔹 Microsoft Purview Data Loss Prevention (DLP)
🔹 Information Protection & Sensitivity Labels
🔹 Auto-Labelling
🔹 Sensitive Information Types (SITs)
🔹 Trainable & Custom Classifiers
🔹 Insider Risk Management
🔹 Device Management & Endpoint Integration

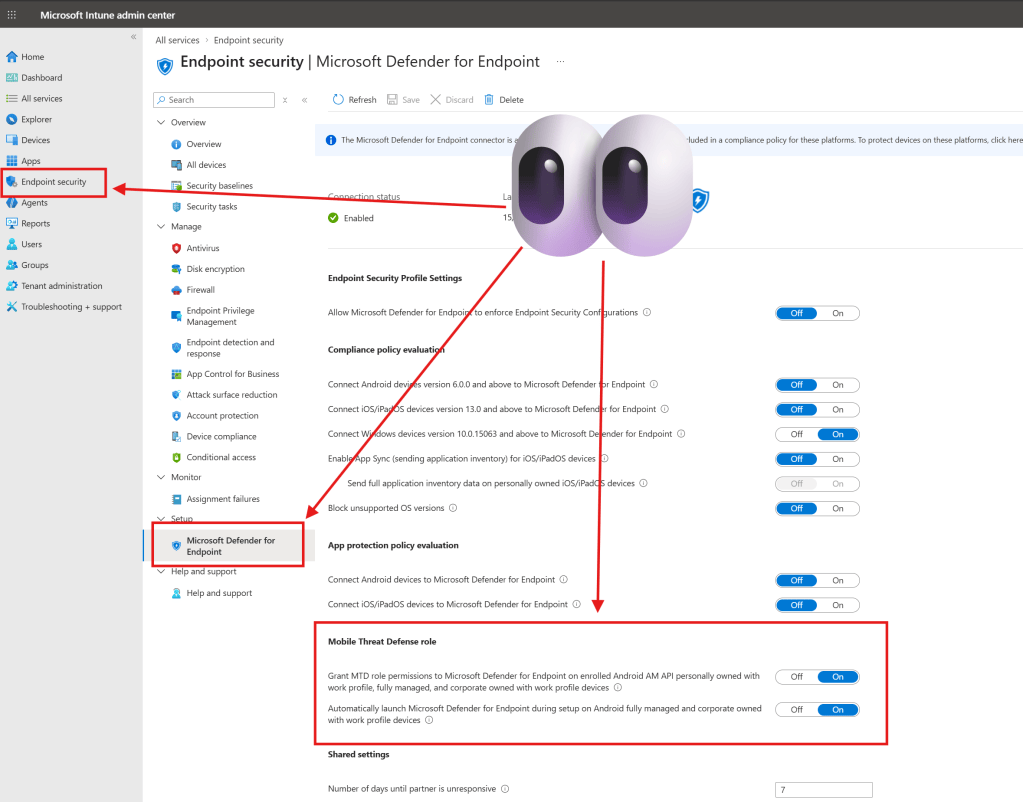
Intune now auto-opens Defender during Android OOBE

Microsoft’s Intune supports Defender for Endpoint onboarding on Android as app-driven, with a device counted as onboarded once the user opens the Defender app and completes setup.

Intune can now open Defender automatically during out of box setup on corporate owned fully managed (COBO) and corporate owned work profile (COPE) devices.

If the user doesn’t finish configuration, the Intune setup step stays available so they can open Defender again.

Note that personally owned work profile devices aren’t supported.

Microsoft Purview Deployment Video Series: Part 2 released

My next Purview video is available to watch now!

In this video, we take the next step in configuring Microsoft Purview by exploring one of the most important concepts in any data protection strategy: data classification.

Before you can apply labels, encryption, retention policies, or data loss prevention controls, you first need to understand what data exists in your environment and why it matters to the business.

In this episode, I walk through the different classification tools available in Microsoft Purview and show you how to use them to identify, organise, and understand your information estate.

In this episode you’ll learn how to:

✅ Understand the difference between classification and labelling

✅ Explore built-in Sensitive Information Types (SITs)

✅ Review how Microsoft Purview automatically classifies data

✅ Create custom Sensitive Information Types using Regex

✅ Reduce false positives with supporting elements and confidence levels

✅ Create Fingerprint-based Sensitive Information Types for structured forms

✅ Understand Trainable Classifiers and AI-powered document classification

✅ Create custom Trainable Classifiers using positive and negative training samples

✅ Review and improve classification accuracy through feedback training

✅ Understand Exact Data Match (EDM) classifiers and their use cases

✅ Trigger SharePoint re-indexing to force reclassification of data at rest

✅ Configure On-Demand Classification scans in Microsoft Purview

✅ Use Data Explorer and Content Explorer to investigate classified data

You’ll also gain an understanding of how Sensitive Information Types, Fingerprint Sets, Trainable Classifiers, and Exact Data Match classifiers work together to build the foundation for Information Protection, Data Loss Prevention, Insider Risk Management, and Records Management policies.

This video is part of a larger series covering:

🔹 Microsoft Purview Data Loss Prevention (DLP)

🔹 Information Protection & Sensitivity Labels

🔹 Auto-Labelling

🔹 Sensitive Information Types (SITs)

🔹 Trainable & Custom Classifiers

🔹 Insider Risk Management

🔹 Device Management & Endpoint Integration

Whether you’re deploying Microsoft Purview for the first time or looking to improve an existing deployment, understanding how to classify data correctly is critical to building effective protection and governance controls.